Corporate Governance – T-Mobile’s Chief Information Security Officer will give regular reports to the board concerning T-Mobile’s cybersecurity posture and business risks posed by cybersecurity. This is a foundational requirement for all well-governed companies. Corporate boards need both visibility and cybersecurity domain experience in order to effectively govern. This commitment ensures that the board’s visibility into cybersecurity is a key priority going forward.
Modern Zero-Trust Architecture – T-Mobile has agreed to move toward a modern zero trust architecture and segment its networks. This is one of the most important changes organizations can make to improve their security posture.
Robust Identity and Access Management – T-Mobile has committed to broad adoption of multi-factor authentication methods within its network. This is a critical step in securing critical infrastructure, such as our telecommunications networks. Abuse of authentication methods, for example through the leakage, theft, or deliberate sale of credentials, is the number one way that breaches and ransomware attacks begin. Consistent application of best practice identity and access methods will do more to improve a cybersecurity posture than almost any other single change.

Khamrah by Lattafa for Men - 3.4 oz EDP Spray
4% Off
Ghost Sweetheart Eau de Toilette | Pineapple, Jasmine and Sandalwood | Perfume for Women 50 ml
50% Off
Marc Jacobs Dot Eau De Parfum for Women, 100 ml
42% Off
Ted Baker W Eau de Toilette for Her, Fig Leaf, White Peony and Violet Top Notes, Pink Orchid and Raspberry Middle Notes, 75ml
£11.77 (£15.69 / 100 ml) (as of 29/10/2026 05:38 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
Ted Baker Woman Pink Eau de Toilette Spray Floral Green Feminine Fragrance, Opening Notes are Fresh Peach, Bergamot and Tangerine with Warm Musk, Vanilla and Vetiver Base, 100ml
11% Off
Vera Wang Princess Eau de Toilette - 30 ml
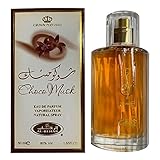
Choco Musk 50ml Eau De Parfum for men and women | Chocolate Musk by Jannat Aromas
17% Off
Christina Aguilera Signature Eau de Parfum (50ml) Floral, Fruity & Exotic Scent, Luxury Fragrance for Women
9% Off
Calvin Klein - Eau De Toilette CKIN2U - Calvin Klein Women, Ladies Perfume, Women's Perfume, Calvin Klein Perfume, Calvin Klein One - 150 ml
5% Off
Jimmy Choo Flash Eau de Parfum, 60 ml (Pack of 1)
3% Off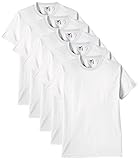
Fruit of the Loom Men's Heavy T Shirt, White, XL UK
28% Off
ATNKE LED Lighted Beanie Cap,USB Rechargeable Running Hat Ultra Bright 4 LED Waterproof Light Winter Warm Gifts for Men and Women/Pink
17% Off
Men's 1/4 Zip Pullover UK Sale Clearance, Fleece Sweatshirt Casual Jumper Long Sleeve T-shirt Top Stand Collar Sweater Plain Pullover Sports Leisure Workwear Quarter Zip Sweater Lightweight Jumpers
£5.88 (as of 11/11/2025 23:52 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
Crevice Cleaning Brush, Bathroom Tile Groove Gap Cleaning Brush,Premium Crevice Cleaning Tool Aluminum Support with 15° Angle Magic Brush, Thin Brush for Home Kitchen
19% Off
Wireless Earbuds, Bluetooth 5.3 Headphones in Ear with HiFi Stereo Deep Bass, 4 ENC Noise Cancelling Mic Wireless Earphones 40H Playtime, Bluetooth Earbuds Dual LED Display, IP7 Waterproof, USB-C
42% Off